
Doing more with limited IT resources
Managed Security
Operations Centre (SOC)
24/7 security monitoring, expert threat detection and rapid response to help protect your business from evolving cyber threats.
Cyber Security Challenges
Why Organisations
Need A Managed SOC
Cyber security tools are an essential part of protecting your business, but technology alone cannot guarantee that threats will be identified and contained before they cause damage.
Security alerts can go unnoticed, sophisticated attacks can evade individual controls, and internal IT teams may not have the time or specialist resources to investigate every potential incident around the clock.
Organisations increasingly need to:
 Detect suspicious activity across devices, identities and business systems.
 Investigate security alerts and distinguish genuine threats from false positives.
- Respond quickly to contain threats before they spread.
- Maintain visibility of security risks outside normal working hours.
- Reduce the pressure on internal IT teams and security resources.
Nearly half of those responsible for cyber security in UK businesses lacked confidence in dealing with cyber security breaches or attacks. Source: UK Government, Cyber security skills in the UK labour market 2026
Xeretec Managed SOC Overview
Security Expertise
That Works Around the Clock
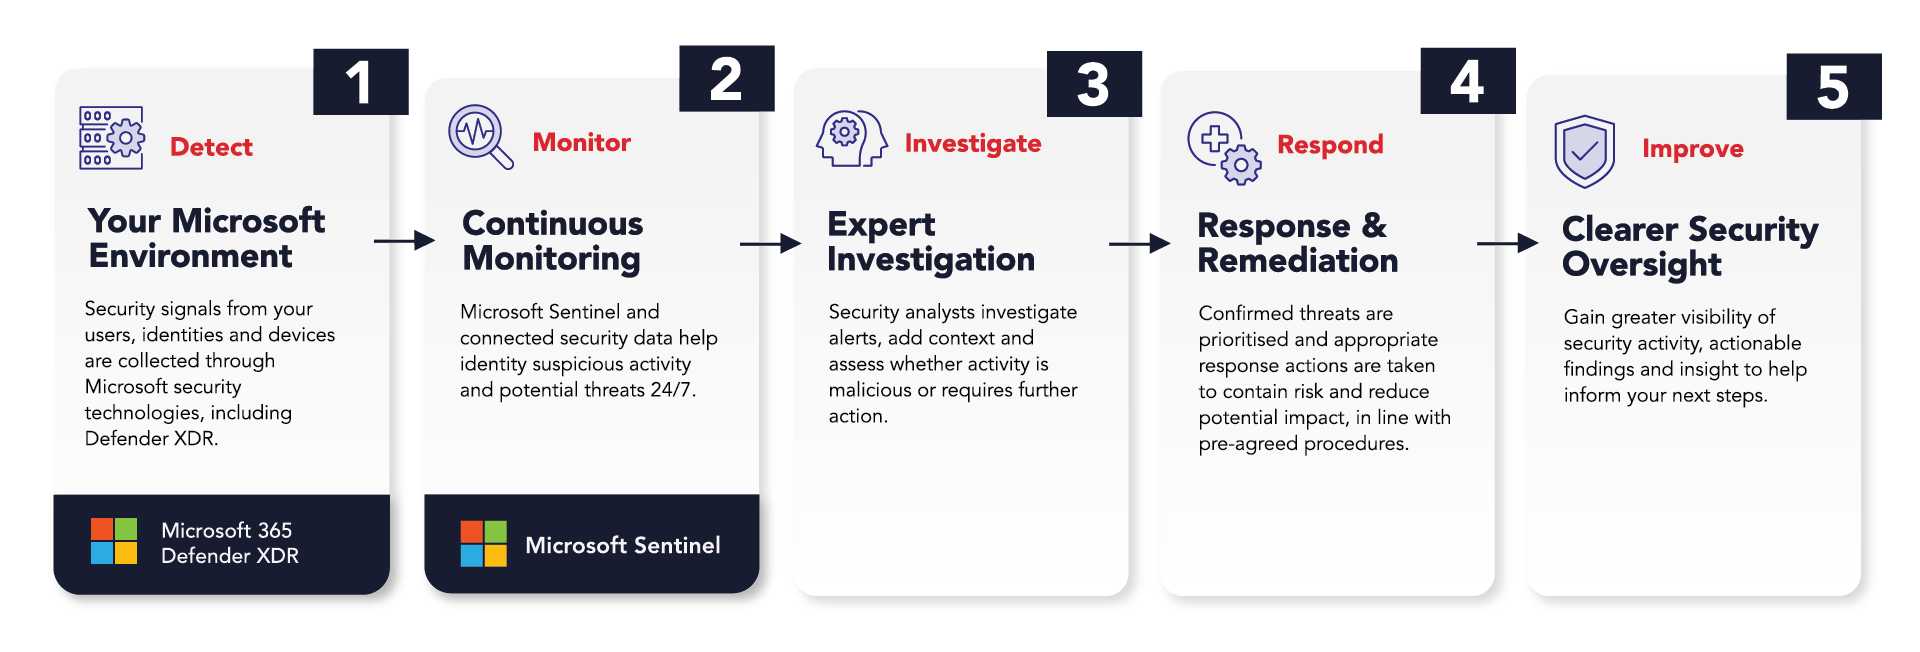
Our Managed SOC provides continuous monitoring and threat detection, with investigation and response focused on protecting endpoints and identities.
It brings together security information from across the wider IT environment, helping security teams identify connections between events and investigate threats that might otherwise go unnoticed.
The service combines Microsoft security technology, automation, threat intelligence and experienced security analysts 24/7/365.
24/7/365 Security Operations
Continuous monitoring through our Cyber Security Operations Centre, with specialist analysts available to investigate and respond to threats beyond normal business hours.
Threat Detection and Investigation
Microsoft security technology, analytics and threat intelligence help identify suspicious activity, investigate alerts and prioritise incidents requiring action.
Automated Remediation
Configured security playbooks and automation can respond to recognised threats, helping contain incidents quickly and reduce manual intervention.
Endpoint and Identity Protection
Detect and respond to threats affecting supported devices, servers and cloud identities, helping reduce the risk of compromised accounts and infected endpoints.
Proactive Threat Hunting
Look beyond existing alerts to investigate suspicious behaviour and indicators of compromise that may otherwise go undetected.
Security Reporting and Governance
Receive service reporting and security recommendations to help inform ongoing risk management, improve visibility and support future security decisions.
How Our Managed
SOC Works
Managed SOC Benefits
Move Beyond Alerts
to Active Protection

Faster Threat Response
Continuous monitoring, automation and specialist investigation help reduce the time taken to acknowledge and resolve security incidents.

Greater Visibility of Threats
Bring relevant security information together to identify suspicious activity across supported devices, identities and systems, reducing gaps in visibility.

Less Pressure on Internal IT Teams
Give your IT team access to specialist security expertise without needing to build and maintain an equivalent in-house security operations capability.

Reduce Alert Fatigue
Use contextual analysis and automated investigation to help prioritise significant threats, rather than requiring your team to investigate every alert manually.

Support for Complex Attacks
Correlate activity across multiple systems to help identify patterns associated with more sophisticated attacks and understand how a threat may be moving through your environment.

A More Proactive Security Approach
Use threat intelligence, threat hunting and ongoing security recommendations to help strengthen your security posture over time.

Built Around Microsoft Security
Leverage Microsoft security technologies, including Microsoft Defender and Microsoft Sentinel where applicable, to integrate protection with your existing Microsoft environment and make better use of supported security capabilities.
Specialist Expertise, Day and Night
Access a dedicated security operations capability operating 24 hours a day, 365 days a year, helping provide continuity of monitoring when your own team is unavailable.
How a Managed SOC Fits Into
Your Security Strategy
Our Managed SOC complements your existing cyber security controls. It does not replace the need for secure configurations, access controls, patching, user awareness or an effective incident response plan.
Working with Xeretec, you can assess your current security arrangements, identify gaps in monitoring and response, and determine the level of managed protection appropriate for your organisation.

FAQs
Find answers to common questions about our Managed SOC services.
A Managed SOC is a service that combines security technology with specialist monitoring, threat investigation and response. It helps organisations identify suspicious activity, investigate potential incidents and take action to contain threats.
No. a Managed SOC is designed to complement your existing security controls. The service uses supported security technologies and configured integrations to improve monitoring, investigation and response. An assessment can establish what you already have in place and what additional capabilities may be needed.
Yes. Chorus provides a 24/7/365 Cyber Security Operations Centre. This supports continuous security monitoring and incident handling outside standard business hours, subject to the agreed service scope and response arrangements.
The service can include supported cloud identities and Microsoft security integrations. Broader SOC coverage can extend to additional cloud services and data sources, depending on the selected service and configuration.
No. Our Managed SOC provides access to specialist security monitoring and response capabilities without requiring you to build an equivalent operation internally. Your existing IT team can continue to manage day-to-day IT and security responsibilities, with the managed service providing additional expertise and support.
A Managed SOC can support security monitoring, incident detection and response processes that contribute to your wider security and compliance objectives. It does not, by itself, guarantee compliance or certification. Requirements should be assessed against the relevant standards, policies and regulatory obligations.
Speak to Xeretec about your current security arrangements, the threats you are most concerned about and the level of monitoring and response you require. We can help establish the appropriate next steps with our specialists.